
Security and access control · RBAC specialist
What Is Role-Based Access Control in Study Library Software?
Design staff access around legitimate responsibilities, resource actions and branch scope—while enforcing authorization on trusted server-side boundaries.
Quick answer
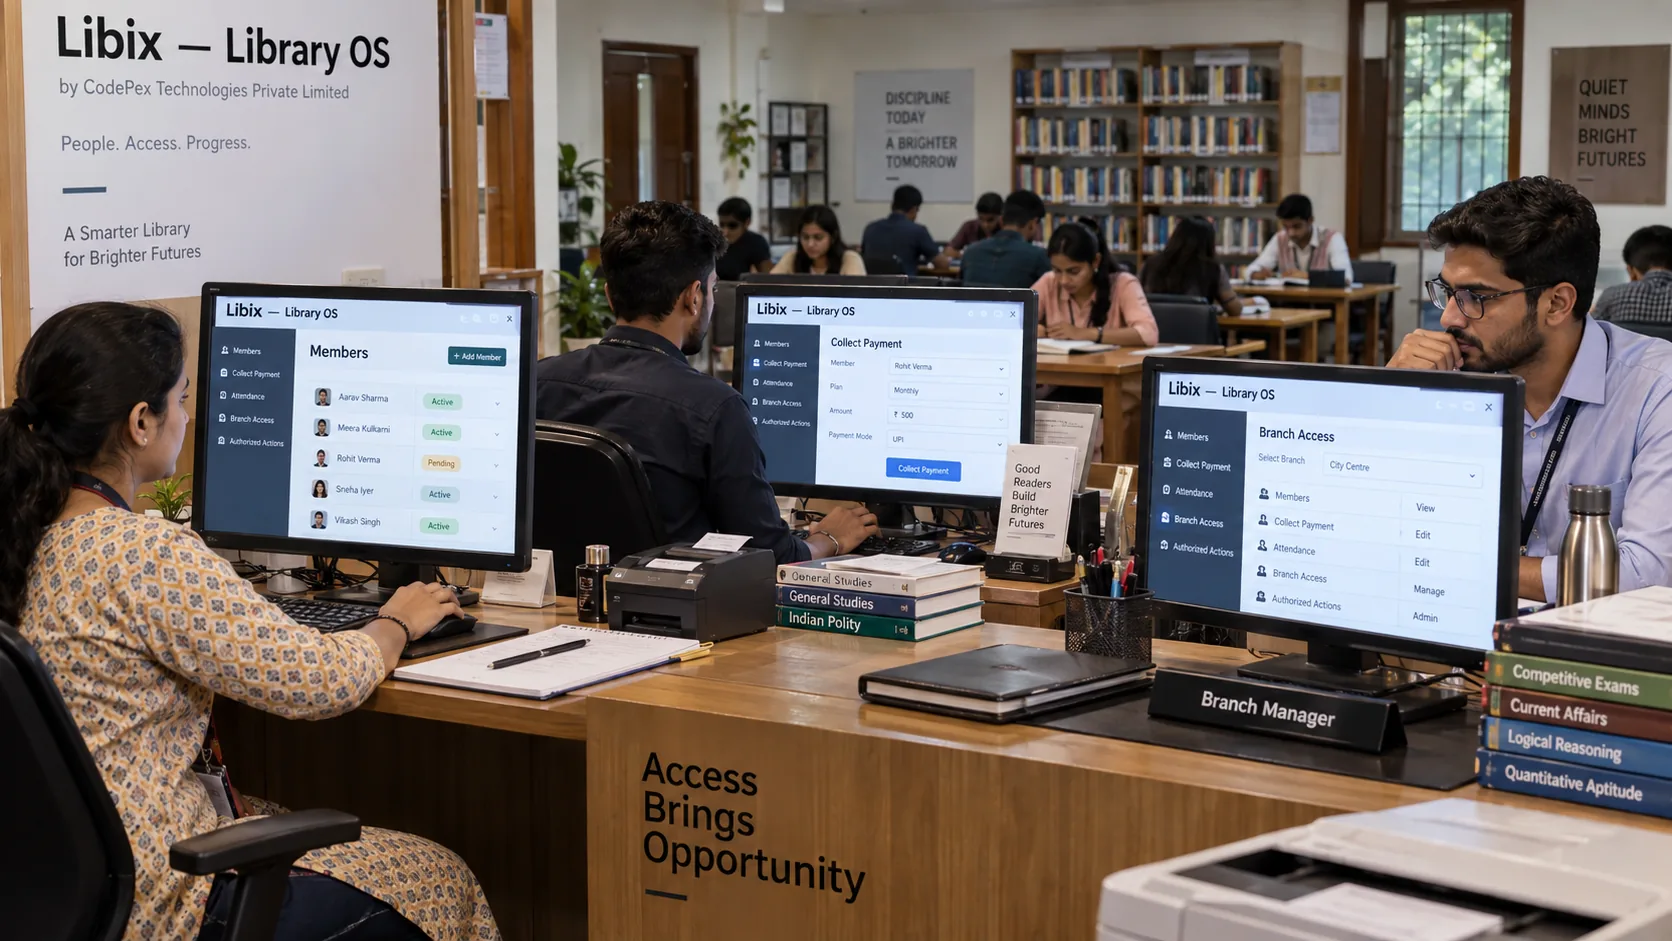
Role-Based Access Control (RBAC) controls what each software user can see and do according to assigned responsibilities. A receptionist might create admissions, record attendance, see seat availability, collect approved payments and print receipts, while refund approval, payroll, role administration and cross-branch finance export remain restricted. In a multi-branch operation, role alone is insufficient; scope matters.
User
A unique software identity
Role
A reusable responsibility grouping
Permission
A specific capability/action
Scope
Where and which records it applies to
Authentication is not authorization
Authentication answers “Who are you?” Authorization answers “What are you allowed to do?” A correctly logged-in user can still be unauthorized to approve a refund. Use unique accounts rather than shared owner or reception passwords wherever practical.
Think in resources, actions and scope
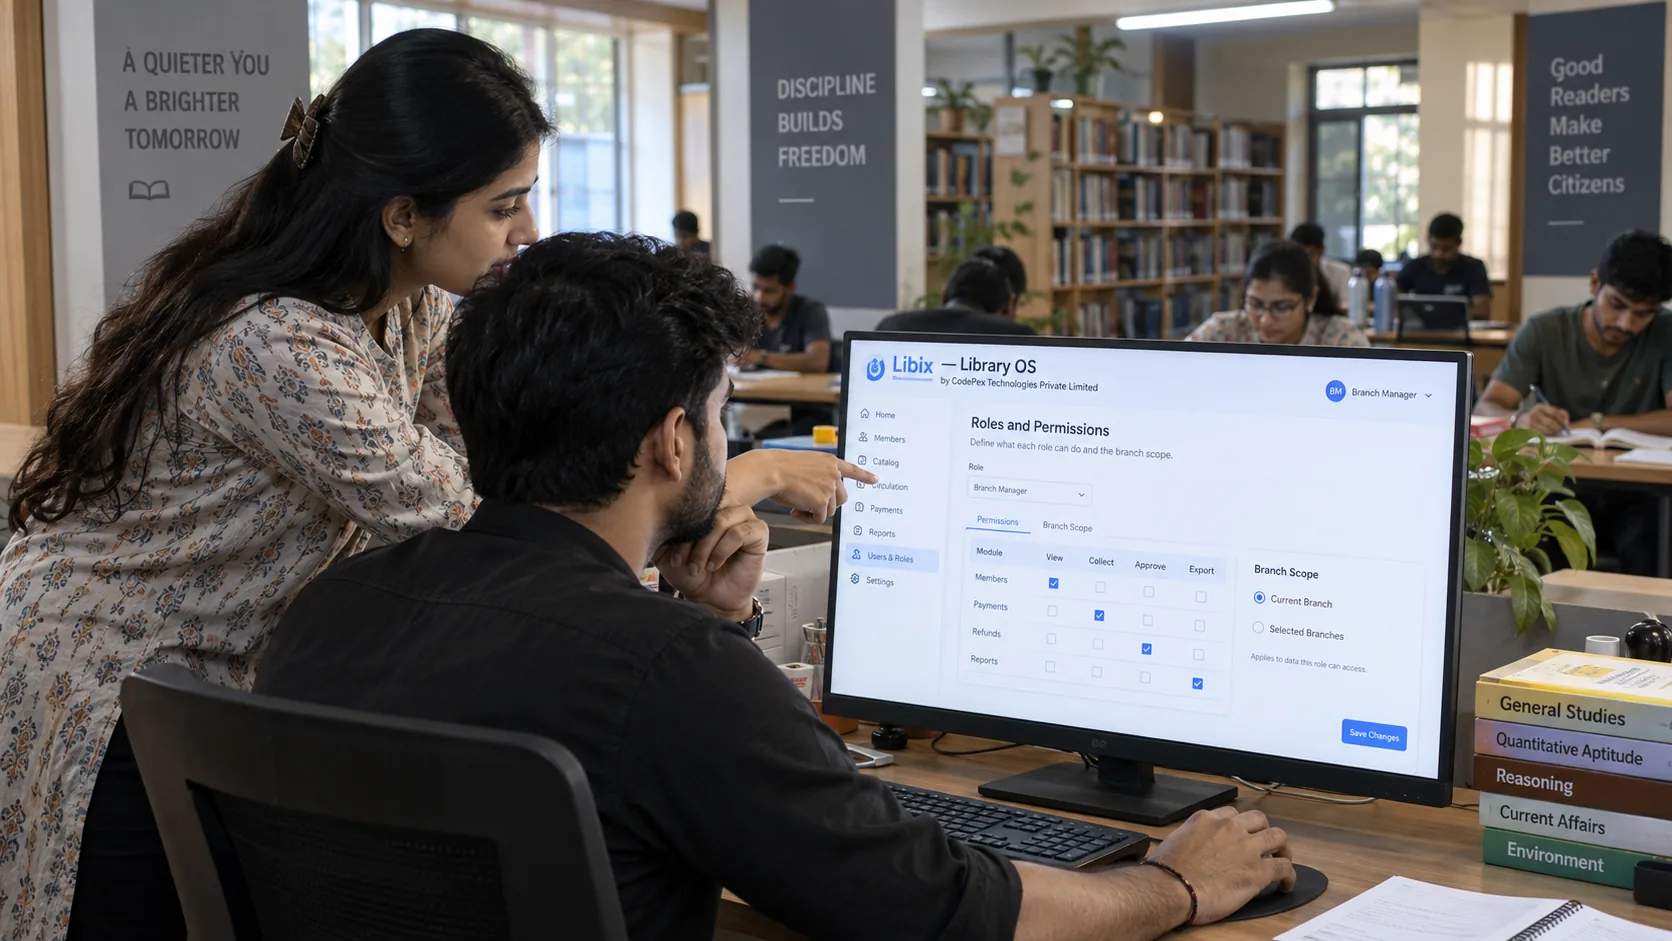
A useful model treats each business domain as a resource and each capability as an action. Members may have read, create, update or archive actions; payments may have read and collect; refunds may have request, approve and execute; reports may have view, print and export. CRUD is not enough for every sensitive workflow.
Scopes can include the current branch, selected branches, organization-wide governance or own/assigned records where supported. A branch selector is not proof of branch authorization; the server must validate the scope.
Example study-library roles
These examples are hypothetical. Design from actual responsibilities rather than copying job titles or creating a giant manager role.
Reception
Member lookup, admissions, attendance, seat availability, approved payment collection and receipt printing; not refund approval or role administration.
Fee collection
View charges, collect payments and issue receipts within an appropriate scope; separate reversal, refund approval and financial configuration.
Operations
Members, attendance, seats, shifts, lockers, announcements and complaints; restrict payroll and security administration.
Branch manager
Broad access inside an assigned branch, not unrestricted access to every branch. Role + scope is more precise than role alone.
Finance
Collections reports, dues, refunds, expenses and reconciliation where assigned; not necessarily permission administration or HR records.
Owner/admin
Broad governance may be legitimate, but avoid shared accounts, permanent emergency credentials and unlogged privileged changes.
Sensitive actions and separation of duties
Distinguish collecting a payment from reversing it, requesting a refund from approving or executing it, viewing a report from exporting it, and managing staff from managing permissions. Small teams may combine duties, but compensate with owner review, reconciliation, audit evidence or other practical controls. Do not declare every combination universally prohibited.
Frontend, server and API enforcement
Frontend permission filtering can improve usability, but hiding a menu or disabling a button is not authorization. A protected server/API operation should validate identity, trusted organization context, branch or resource scope, permission, target resource, workflow state and any contextual rule. Missing permission, unknown role, unresolved tenant or malformed scope should fail safely rather than grant access.
Role design, changes and review
List job functions, resources and actions; identify sensitive actions; define tenant and branch scopes; group permissions into roles; separate conflicting duties; assign roles; enforce them server-side; test allowed and denied cases; review access; and revoke or adjust access when responsibilities change.
Temporary access
Reason, scope, start/end, approval, expiry and review where supported.
Offboarding
Disable account, revoke sessions, remove roles, transfer work and preserve history.
Periodic review
Review privileged roles, cross-branch access, exporters, refund approvers, role editors, former staff and temporary grants.
Test allowed and denied cases
Positive tests are only half the job. Test wrong branches, wrong organizations, direct API calls, expired temporary grants, workflow-state violations, refund approval boundaries, report export, role assignment and stale sessions after a role change. RBAC is not audit logging, encryption or complete security; it is one authorization layer.
Common mistakes
Where Libix fits
Verify the actual authorization surface
Libix—Library OS is study-library management software from CodePex Technologies Private Limited. Current users, roles, permission definitions, branch and tenant scope, route guards, API authorization, multi-role behavior, role-change invalidation and denied-access logging must be verified against the repository and approved documentation. This page does not invent permission keys or claim that RBAC alone secures the product.
Access-design lab
Draft a role without changing real accounts
This is an educational role-design aid. It does not configure Libix, call APIs, inspect users, grant privileges, produce a security score or determine legal compliance.
Hypothetical role and scope
Sensitive actions for review
Permission matrix for Reception
Select only actions justified by actual responsibilities. Examples are illustrative, not Libix permission keys.
Reception
Admissions
Memberships
Attendance
Seats/shifts
Lockers
Fee collection
Refunds
Communication
Complaints
Staff
Payroll
Finance
Reports
Settings
Access administration
Review combinations
No flagged combination from the current hypothetical selections. Review is still required.
Implementation questions
Are permissions enforced server-side? Does scope apply to every resource? Are direct API calls denied? Are role changes and offboarding reviewed?
Frequently asked questions
What is RBAC in study-library software?
Role-Based Access Control connects a unique user to one or more roles, permissions and scopes so legitimate work can be allowed while unnecessary access is denied.
Is hiding a menu enough?
No. The server and APIs must enforce identity, organization, branch, permission, resource and contextual rules. Frontend filtering improves usability but is not the security boundary.
Should every administrator have every permission?
Not automatically. Separate permission administration, financial approvals, staff management and sensitive settings where practical, while using compensating controls for smaller teams.
Should collecting payments and approving refunds be separate?
They can be separate actions and duties. The right design depends on the workflow; review combinations rather than applying an absolute rule to every library.
How should former staff access be removed?
Disable the user, revoke sessions where applicable, remove roles, transfer workflow ownership, rotate relevant shared secrets and preserve access-change history.
How does RBAC relate to Libix?
Current Libix user, role, permission, branch-scope, route-guard and API-authorization behavior must be verified against the repository and approved documentation before being described as implemented.